THE MINIMUM CYBER SECURITY EVERY SME NEEDS

A Practical Application of the Cyber Essentials UK Scheme

A practical guide that helps small and medium-sized businesses turn cyber security concepts into concrete controls that protect their operations.

Based on Cyber Essentials v3.3 — NCSC / IASME Consortium

Cover of the book The Minimum Cyber Security Every SME Needs, by Ricardo Córdoba Baptista

About the book

It almost always starts with a simple failure

One click on a fake link, a reused password or an unpatched program is enough to bring operations to a halt.

Small and medium-sized businesses have become a favourite target for cyber criminals. One click on a fake link, a password reused across several systems or a program that has not been updated is enough to bring operations to a halt, expose customer data and open the door to fraud. Almost always, the problem starts with a simple failure that could have been fixed.

The Minimum Cyber Security Every SME Needs is a practical information security guide written for two audiences: those who have never dealt with the subject, and those who already work in the field and need a proven standard to guide their own organisation or their clients.

It starts from Cyber Essentials, the scheme created by the UK government to define the baseline level of cyber security that every organisation should have, and shows how to apply it to the reality of smaller businesses, in clear language and without jargon.

Minimum viable security

Cyber security starts with the basics

“Those who chase perfection end up putting off every initiative. Those who implement the essentials need to start with what they can actually implement, maintain and sustain.”

Small and medium-sized businesses do not need to start with the perfect architecture. They need to start with the controls that genuinely reduce their exposure. The book applies the logic of the minimum viable product to cyber security: implement the minimum necessary first, with discipline and consistency, and build from there. It is not a guarantee against every attack, but a solid foundation on which a business can grow.

Cyber Essentials

The five core controls

The technical core of Cyber Essentials: five controls that, when properly implemented and maintained, reduce a business's exposure to the most common attacks.

Diagram: the five Cyber Essentials controls arranged around a central shield 1 2 3 4 5
  1. 01. Firewalls

    Control what enters and leaves the network and each device, closing ports and services that do not need to be exposed to the internet.

  2. 02. Secure configuration

    Removes unnecessary accounts, software and features, changes default passwords and adjusts devices so they are not left open as they come from the factory.

  3. 03. Security update management

    Keeps systems and applications supported by the vendor and applies critical security fixes within a short timeframe.

  4. 04. User access control

    Ensures each person has only the access they need, with strong authentication and separate administrator accounts.

  5. 05. Malware protection

    Prevents malicious software from being installed or run, using active anti-malware or an allow list of approved applications.

More than the five controls

What you will find inside

Beyond the technical controls, the book covers backups, incident response, security culture, the UK GDPR and how to get started.

  1. The 5 Cyber Essentials controls

    Firewalls, secure configuration, security updates, user access control and malware protection, explained in detail.

  2. What needs protecting

    How to define the scope, from the office network to cloud services, home working and personal mobile phones used for work.

  3. The threats that hit SMEs hardest

    Ransomware, phishing, leaked passwords and other attack vectors relevant to small and medium-sized businesses.

  4. Backup and recovery

    How to set up backups that can survive a ransomware attack.

  5. Incident response

    A practical guide to what to do in the first thirty minutes of an incident.

  6. Security culture

    How to make security a routine, not just a tool.

  7. UK GDPR and security

    What the UK GDPR requires on security, and how to handle personal data breaches, the ICO and the people affected.

  8. A plan for the first 90 days

    A step-by-step roadmap to start structuring the business's security.

  9. Checklists and guides

    Checklists throughout the book and guides to help the business ask its IT provider for the right measures and check that they are in place.

Controls and certification

A reference for putting controls in place and working towards certification

  • Question by question

    The chapters on the controls follow, question by question, Danzell, the 2026 question set used by the IASME Consortium for the Cyber Essentials self-assessment.

  • What the assessor expects

    Each chapter opens with a map of the questions covered and explains what each question is looking for, which answer is accepted and what evidence the assessor expects to see.

  • Policies and procedures

    Beyond the technical side, the book includes template policies and procedures to adapt to the business's own situation, such as an information security policy.

  • Cases and references

    Each topic is illustrated with real cases, and the text brings together quotations and academic references for readers who want to explore further.

Audience

Who is this book for?

Business owners and managers

For those who have never organised their business's security. The book turns each control into management decisions and shows what to ask, what to require and how to check it has been done, without needing to master the technical side.

IT and security consultants

For professionals who serve small and medium-sized businesses and need a minimum baseline to organise assessments, set priorities and explain to clients, in business language, why each measure matters.

Lawyers

For lawyers who advise businesses and need to understand basic security controls in order to draft contracts with technology suppliers, advise on UK GDPR matters and act in the event of incidents or regulatory inspections.

Service providers

For service providers who need to put minimum protection in place with limited resources, including when larger clients require evidence of security across their supply chain.

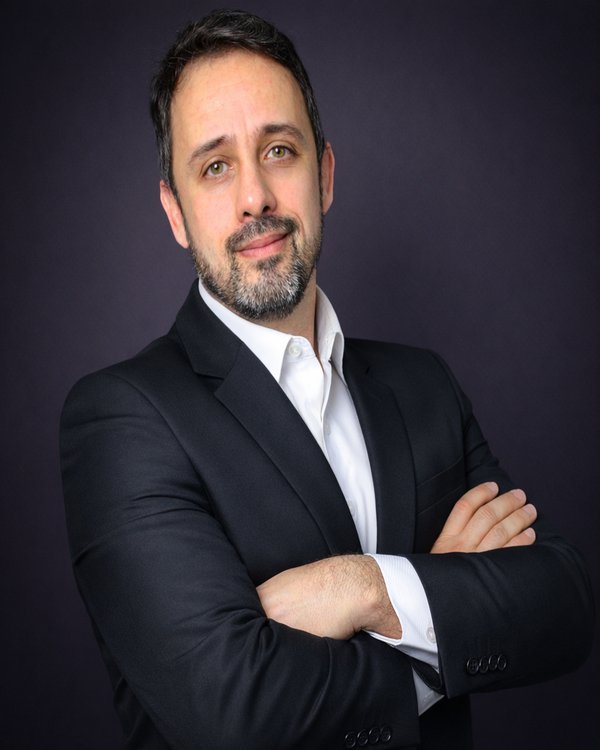
Photograph of Ricardo Córdoba Baptista

The author

Ricardo Córdoba Baptista

Digital law and information security

A lawyer specialising in digital law, cyber security, privacy, data protection and digital fraud, Ricardo Córdoba Baptista brings together both the technical and the legal perspectives of information security.

He has worked in this field for more than twenty years, and that experience shapes the book's practical approach.

Blog

Reading to get you started

Short articles on information security for small businesses, written for people who need to decide and act.

Start with the minimum.

It is what keeps your business sustainable.

Discover the book

Does your business already know what the minimum is?

Start with the controls that need to be working before an incident forces your business to start.

Buy on Amazon